Security assessment
A fixed-scope posture review with a prioritised, costed remediation plan.
Fixed scopePrioritisedCosted
Practical security assessment, hardening, cloud protection and monitoring for regional organisations — aligned with NCA, SAMA and ISO 27001 expectations.
Ethical testing across applications, infrastructure, APIs and mobile.
Prioritised discovery with clear, actionable remediation guidance.
Secure configuration, access controls and disciplined patching.
Secure design, posture management, encryption and identity on AWS and Azure.
Threat visibility, alerting and incident-response readiness.
Risk programmes aligned with NCA, SAMA, ISO 27001 and regional standards.
Riyadh's leading AI-first agency — one accountable in-house team, from first strategy to 24/7 operation. We design, engineer and operate enterprise websites, platforms, mobile apps and private AI for the region's leading brands, with security, compliance and performance built in from day one.
Anyone can hand over a scanner report. We point you at hardened environments — tested by ethical hackers, monitored by SIEM and standing up to real audits across Saudi Arabia. Then let's talk about yours.
The model should match your risk profile and team, not the vendor preference.
A fixed-scope posture review with a prioritised, costed remediation plan.
Focused ethical testing on the systems that matter, with retesting after fixes.
Continuous monitoring, SIEM and response under a monthly agreement — your security operations, run for you.
Gap analysis against NCA, SAMA or ISO 27001, then the controls and evidence to get there.
Plenty of vendors sell scanners. A team that tests, hardens and then continuously operates your security — under one roof — is rarer.
 In-house teamEngineers and security specialists sit together — findings turn into fixes, not PDFs.
 We secure what we buildThe same team engineers enterprise platforms, so remediation is practical, not theoretical.
 Framework fluencyNCA, SAMA and ISO 27001 expectations translated into real controls and real evidence.
 Regional understandingSaudi and KSA regulatory context, data residency and sector expectations as first-class inputs.
 Prioritised by riskFindings ranked by business impact — fix what attackers would actually use first.
 Your evidence is yoursReports, configurations and documentation handed over in full — audit-ready, always.
Controls mapped to NCA, SAMA and ISO 27001 from day one.
Hosting and data-flow decisions mapped to Saudi and KSA rules.
Identity, tunnels and least-privilege access — no open inbound ports.
Every test, change and access logged and reviewable.
A security posture assessment across applications, infrastructure, cloud and people.
Ethical penetration testing on apps, APIs, mobile and networks — with prioritised remediation, not just findings.
Close the gaps: configuration, identity, encryption and network segmentation.
Controls and documentation mapped to NCA, SAMA and ISO 27001 expectations.
SIEM deployment, log pipelines and alerting tuned to your environment.
Incident-response runbooks, escalation paths and 24/7 readiness under agreement.
A selection of enterprise websites, platforms and apps we have designed, engineered and operated across the region.
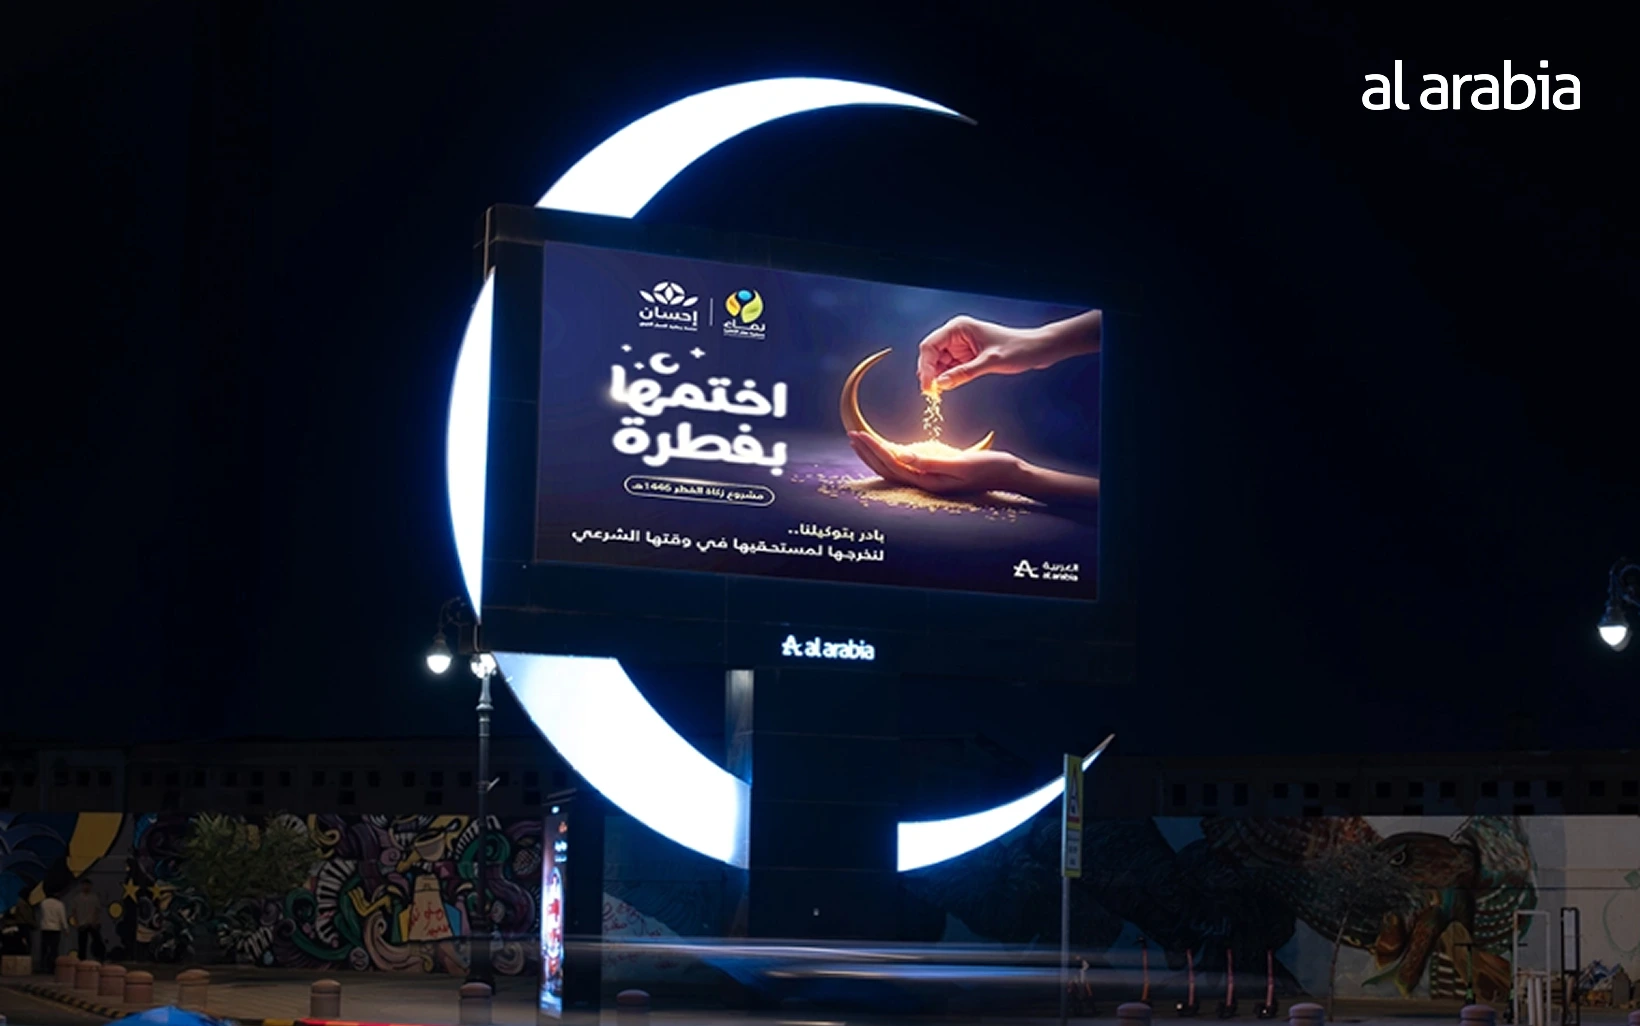
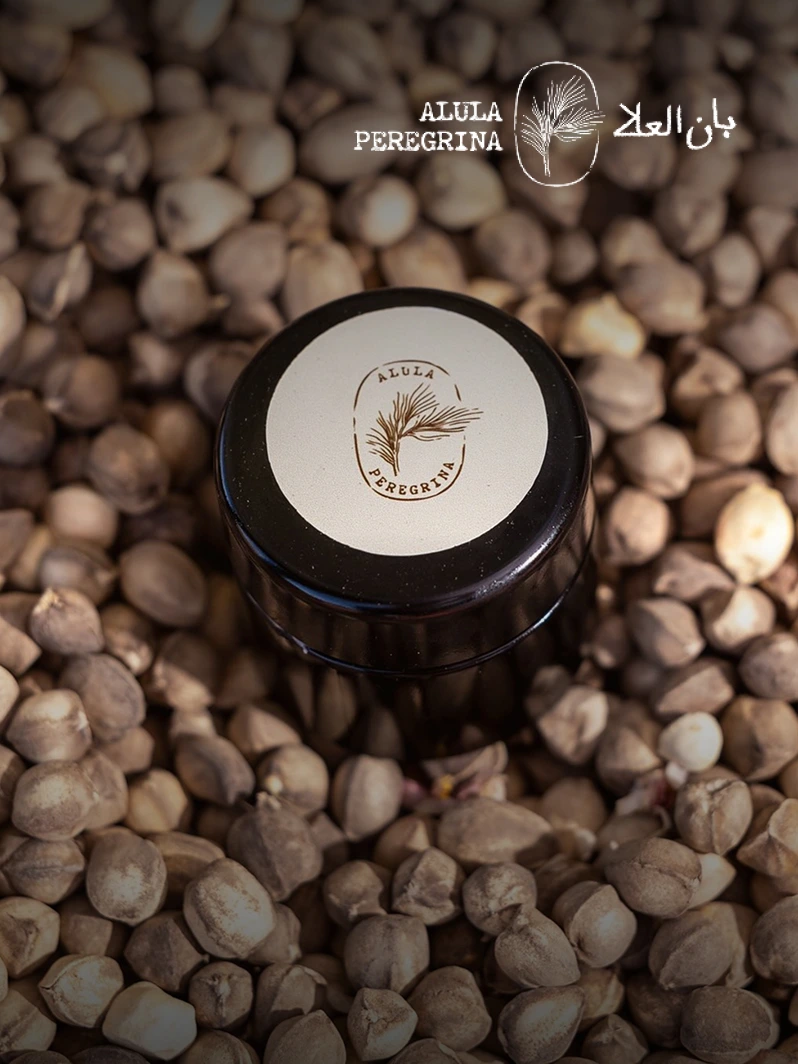
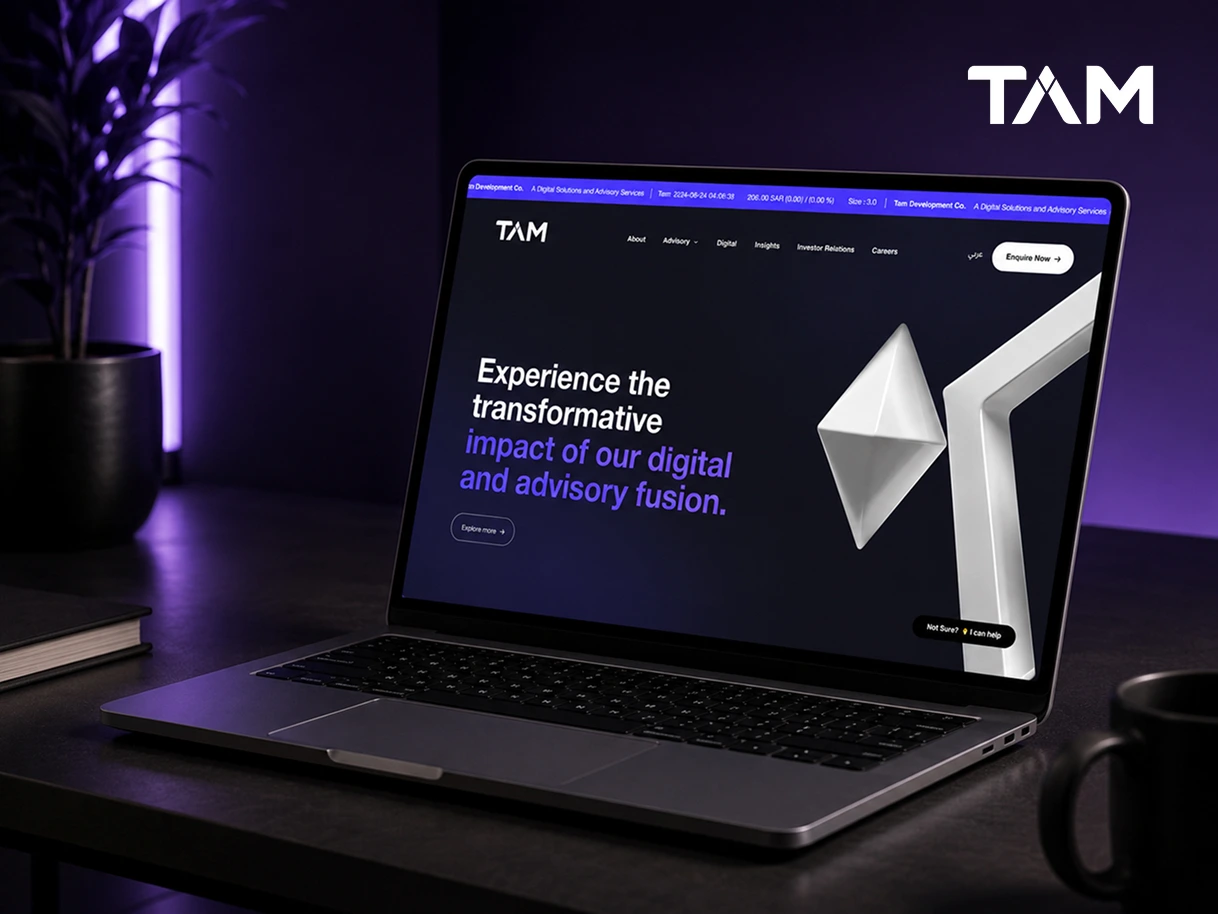
Every capability above is backed by environments under active protection — so we understand your threat profile faster, then shape controls around what attackers actually target.
SAMA-aligned controls, transaction security and fraud-resistant architecture.
NCA-aligned posture, data residency and sovereign hosting decisions.
Patient-data protection, consent flows and access governance.
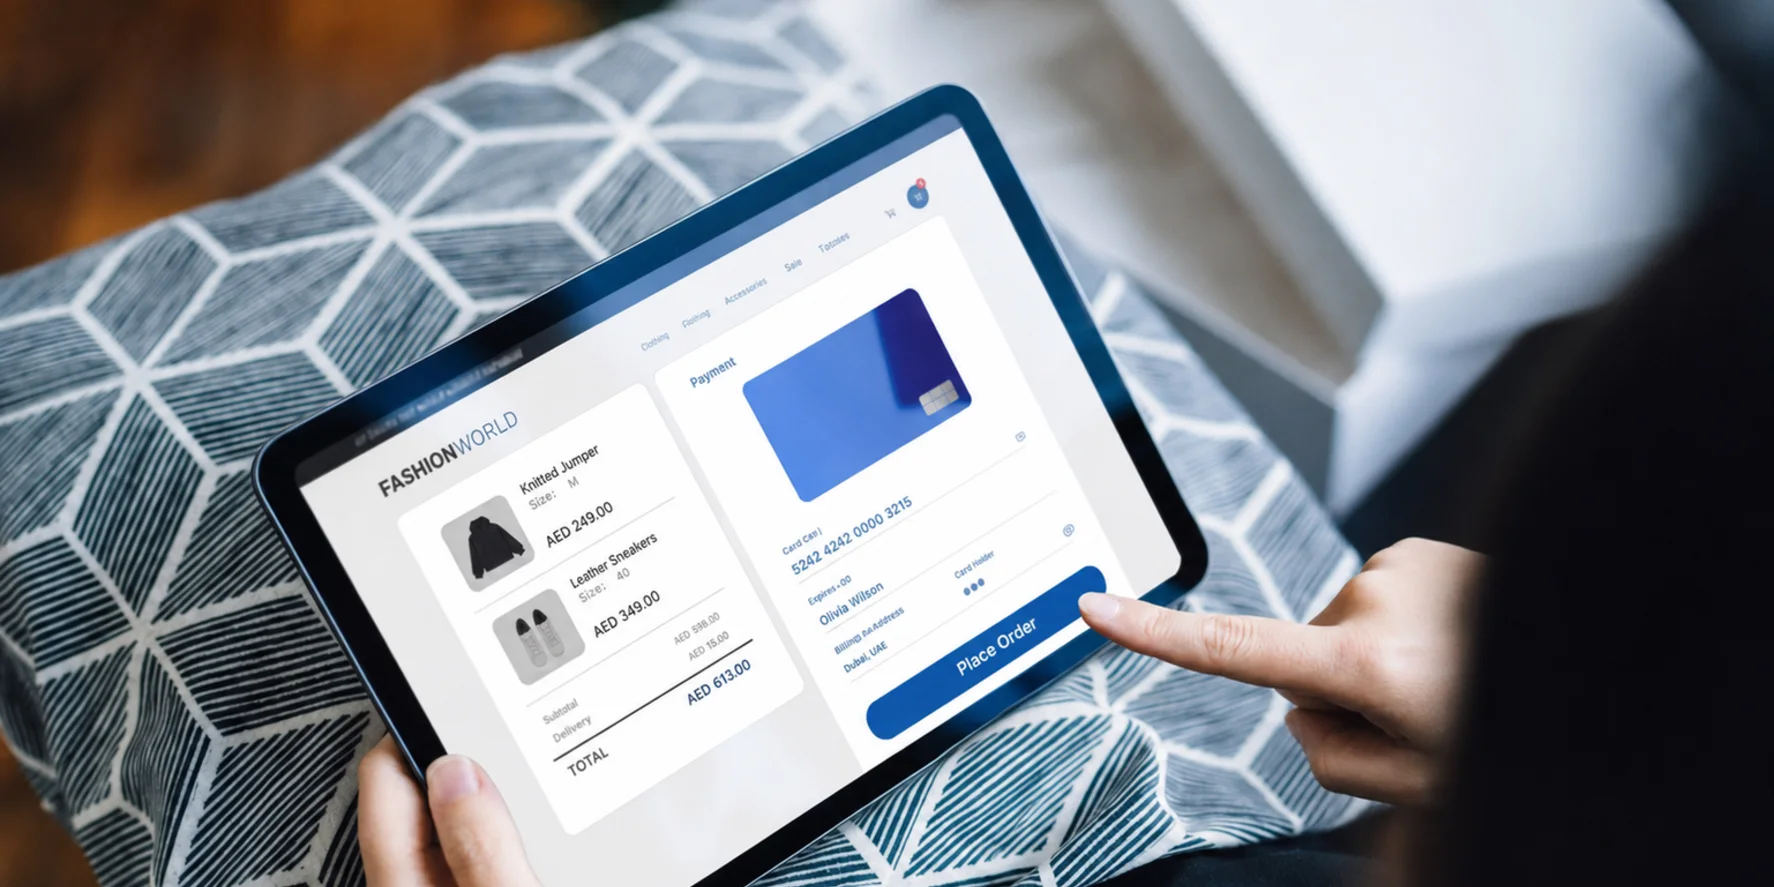
Payment security, PCI-aware architecture and peak-season resilience.
IT and OT segmentation, identity governance and supplier risk.
Student-data privacy, campus systems and safe digital learning platforms.
Attackers rarely need zero-days — expired certificates, weak identities and unpatched services are enough. Find the gaps before someone else does.
a security consultation — tell us what you run and leave with posture findings and a prioritised plan. Critical issues are flagged immediately.
Outcomes from environments this team tests and monitors today — closed gaps, not glossy reports.
“A finding without a fix is homework. We walk the remediation with your team until the gap is closed and retested.”
“Boring is the goal. When the SIEM is quiet and audits pass without drama, security is working.”
Digital transformation is a partnership, not a project.
NCA, SAMA and ISO 27001 expectations, with advisory to close the gaps.
Yes — ethical testing across applications, infrastructure, APIs and mobile, with prioritised remediation.
Yes. Secure design, posture management, encryption and identity on AWS and Azure.
Yes. Threat visibility, alerting and incident-response readiness under managed agreements.
Tell us what you run — applications, infrastructure, cloud. We reply within one business day; critical findings are flagged immediately.
Your brief is in. Our security team will reply within one business day, and your posture findings follow within five working days. If it is urgent, reach us on WhatsApp.
WhatsApp us